Methodology

Capturing malware from honeypots - Advanced In-The-Wild Malware Test

ico top methodology
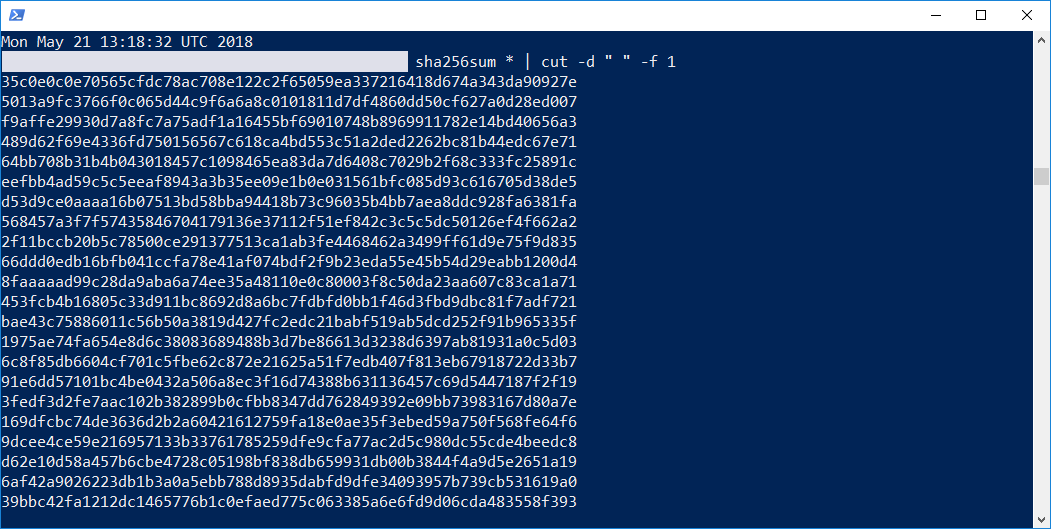
malware sah256 sum
Malicious software collected from one of the honeypots.
An ideal source of samples is this which offers the most widespread, fresh, and diverse samples that are independent of antivirus software provider. In this case, “the freshness“ of downloaded samples/URLs is very important because it affects actual protection against threats which can be found on a daily basis on the Internet. Samples used in „Advanced In-The-Wild Malware Test” come from public malicious URL feeds and attacks on our honeypots network. Honeypots are traps which task is to simulate a target that is vulnerable to attacks and to capture malicious software. We use low (Dionaea, SHIVA, HoneyDB) and high interactive honeypots. All of them emulate services such as: SSH, HTTP, HTTPS, SMB, FTP, TFTP, real Windows systems, and email servers. A lot of interesting information about honeypots can be found on CERT Poland website.

Before every sample goes to machines with security products installed, it should be thoroughly analyzed by static Yara rules scanning and Linux tools. We have to make sure that only 100% harmful samples are included in tests. We provide examples of malicious indicators being introduced by malware into a system:

An attempt to disable UAC:

HKLM\SOFTWARE\Microsoft\Security Center\UacDisableNotify

Adding to autostart:

Software\Microsoft\Windows\CurrentVersion\Run

Swapping wallpaper:

Control Panel\Desktop\Wallpaper

Checking bios version:

Hardware\description\system\bios

Bypassing UAC:

Classes\exefile\shell\runas\command\isolatedCommand

Launching from recycle bin:

C:\$Recycle.Bin

Removing logs:

C:\$GetCurrent\Logs

A situation when a virus won’t operate in a system, because it was programmed for other geographical area, will never happen in our tests. Readers and developers are ensured that malware which was qualified for tests will be able to seriously infect operating systems, regardless of which part of the world it comes from.

Before a potentially harmful sample is qualified for tests, one of the components of a testing system checks if malicious software certainly introduces unwanted modifications. For this purpose, every virus is analyzed for several minutes. The human factor excluded from tests makes it impossible to ascertain whether, for example, malware will finish its activity after 60 seconds. We must establish some time threshold after which we stop an analysis. We are aware that there’s malicious software that can delay its launch up to several hours before it’s activated. It can also listen to connections with C&C server on an ephemeral port. There were also situations when malware was programmed to infect a specific application, or it was waiting for a website to be opened. For this reason, we took every effort to ensure that our tests are as close to reality as possible, and samples which are “unreliable” won’t be included in a test virus database.

After analyzing every potentially malicious sample, logs from the activity of malware are exported to the outer part of the testing system. On the basis of the data gathered, developed algorithms decide whether a particular sample is certainly harmful. We publish part of the information from an analysis on the AVLab’s website in an accessible form for users and developers. Detailed data are shared with developers.

Test Participation & Certification Options

Vendors can participate directly in the Advanced In-The-Wild Malware Test or obtain a Certification-Only Package for a product independently tested by AVLab. Paid participation provides access to extended technical services, test data, and custom configuration options, while result review and verification remain available to all tested vendors.

Advanced In-The-Wild Malware Test - What Is Included?

Paid Assessment Participation
Certification-Only Package

GENERAL

Advanced In-The-Wild Malware Test
Previously performed by AVLab
Public test results
Certification, if criteria are met
Annual awards, if eligible

RESULT REVIEW & TRANSPARENCY

Result review and clarification
Available to all tested vendors
Evidence necessary to verify a disputed result
Available to all tested vendors
Vendor commentary and response
Available to all tested vendors

TEST PREPARATION & CUSTOM CONFIGURATION

Product onboarding and configuration review
Not applicable
Vendor-recommended product configuration
Not applicable
Custom logging configuration
Not applicable
Vendor-requested technical logs
Not available retroactively

TECHNICAL SERVICES AND DATA

Detailed technical analysis
Available separately
Detailed test data
Available separately
API access to test data
Available separately
Evidence & technical logs
Available separately
Additional validation and retesting
Depending on scope
Available separately
Technical consultation with AVLab
Available separately

CERTIFICATION & MARKETING RIGHTS

Official certificate issued by AVLab
Certification badge
Use on vendor website
Use in social media and PR
Use in sales and marketing materials
Annual award materials, if eligible

Commercial use of AVLab certificates, certification badges, and award materials by independently tested vendors requires either Paid Assessment Participation or a Certification-Only Package. Independently tested vendors without either option may be listed in AVLab results and certification records but are not granted the right to use AVLab certification materials in their own marketing or communications.